Comprehensive Security Services

Enterprise-Grade Cybersecurity Services

From VAPT to 24/7 SOC operations, we provide end-to-end security solutions tailored to your organization's unique needs. Explore our integrated security platform and proven methodology.
500+
Clients Protected
1M+
Threats Mitigated
50+
Security Experts
10+
Years Experience
VAPT Services
10,000+
Vulnerabilities Found
500+
Systems Tested
99.8%
Success Rate

VAPT Services

Vulnerability Assessment & Penetration Testing

Comprehensive security testing across all attack surfaces to identify and remediate vulnerabilities before attackers exploit them.
Web Application Testing
Mobile App Security
Network Penetration
API Security Testing
Cloud Infrastructure
Social Engineering
Identify vulnerabilities before attackers do
Comply with security standards and regulations
Reduce risk of data breaches
Detailed remediation guidance
Connect With Us
Application & Cloud Security
1,200+
Apps Secured
300+
Cloud Accounts
5,000+
Misconfigs Fixed

Application & Cloud Security

Secure Your Digital Assets

End-to-end application and cloud security solutions including SAST, DAST, CSPM, and secure development practices.
SAST & DAST
CSPM Solutions
Container Security
DevSecOps Integration
Secure Code Review
API Gateway Security
Shift-left security in development lifecycle
Automated vulnerability detection
Cloud misconfigurations prevention
Continuous security monitoring
Connect With Us
Infrastructure & Network Security
800+
Networks Secured
1M+
Threats Blocked
99.99%
Uptime

Infrastructure & Network Security

Protect Your Network Perimeter

Advanced network security solutions including firewalls, intrusion detection, and network segmentation.
Next-Gen Firewalls
IDS/IPS Systems
Network Segmentation
VPN & Remote Access
DDoS Protection
Zero Trust Architecture
Prevent unauthorized network access
Real-time threat detection and blocking
Secure remote workforce
Reduced attack surface
Connect With Us
OT Security
4+
Sectors Served
IEC 62443
Framework
Passive
Discovery

OT Security

ICS, SCADA & Critical Infrastructure Protection

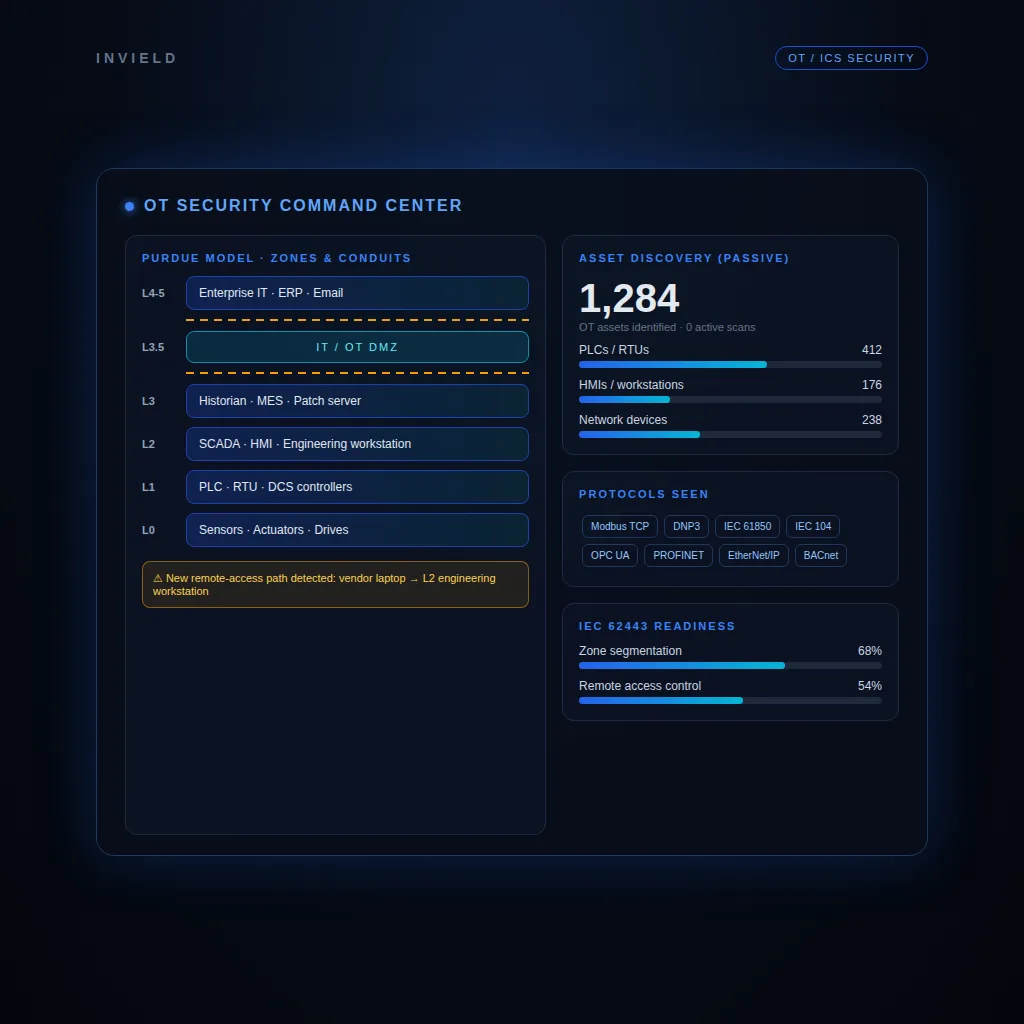
Proven OT and industrial control system security for our partners in the energy & power, manufacturing, aviation and defence sectors — passive asset discovery, IEC 62443 risk assessment, safe OT VAPT and IT/OT segmentation without disrupting operations.
OT Asset Discovery
ICS / SCADA Risk Assessment
Safe OT VAPT
IT/OT Segmentation
Remote & Vendor Access
Energy · Aviation · Defence
Visibility of every PLC, RTU, HMI and controller — without active scans
Risk ranked by safety, production and business impact
Alignment with IEC 62443, NIST SP 800-82 and CEA power-sector guidelines
Experience across energy & power, manufacturing, aviation and defence
Explore OT Security
Security Tool Deployment
200+
Tools Deployed
10M+
Events/Day
85%
MTTD Reduction

Security Tool Deployment

SIEM, SOAR, XDR Implementation

Deploy and manage enterprise security tools for unified threat detection, response, and orchestration.
SIEM Implementation
SOAR Platforms
XDR Solutions
Threat Intelligence
Security Analytics
Automated Response
Centralized security visibility
Automated threat response
Reduced mean time to detect (MTTD)
Improved SOC efficiency
Connect With Us
Incident Response & Threat Intelligence
2,500+
Incidents Handled
< 15min
Avg Response Time
100%
Recovery Rate

Incident Response & Threat Intelligence

24/7 Security Operations

Rapid incident response capabilities with continuous threat intelligence monitoring and analysis.
24/7 SOC Operations
Incident Response
Forensic Analysis
Malware Analysis
Threat Hunting
Breach Notification
Minimize breach impact
Rapid containment and recovery
Proactive threat hunting
Regulatory compliance support
Connect With Us
DFIR — Digital Forensics & Incident Response
IRR
Retainer
Chain of custody
Evidence
CERT-In 6h
Reporting

DFIR — Digital Forensics & Incident Response

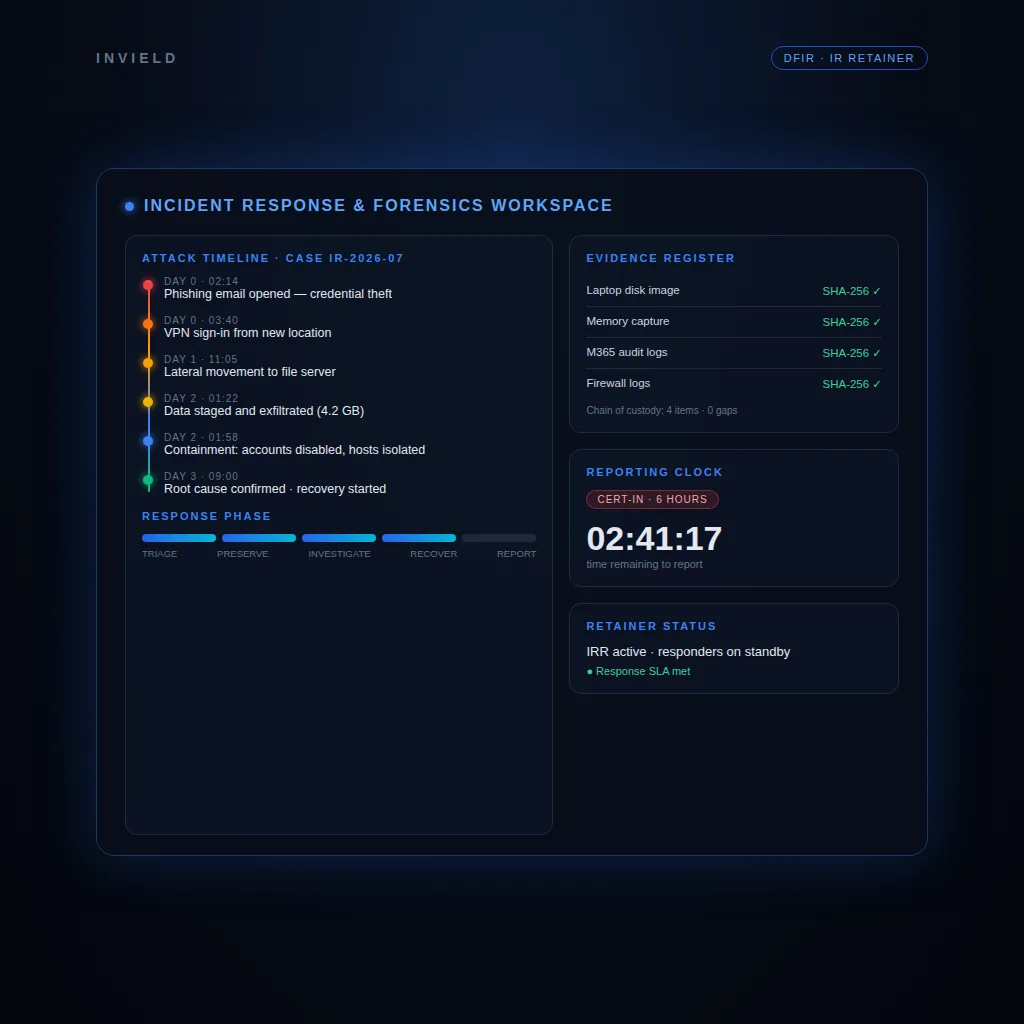
Incident Response Retainer, Forensics & Investigations

Be ready before an incident with an Incident Response Retainer (IRR), and get expert help when it happens — ransomware and breach response, digital forensics, cyber investigations and court-ready evidence.
Incident Response Retainer
Ransomware & Breach Response
Digital Forensics
Cyber Investigations
Compromise Assessment
Expert Reports & Litigation Support
Responders on standby with agreed response times
Forensically sound evidence with documented chain of custody
Support for CERT-In and DPDP Act breach notifications
Discreet insider, fraud and data-theft investigations
Explore DFIR Services
Dark Web Monitoring
15,000+
Leaks Detected
5M+
Credentials Monitored
3,000+
Early Warnings

Dark Web Monitoring

Continuous Threat Surveillance

24/7 monitoring of dark web forums, marketplaces, and channels for compromised credentials and data leaks.
Credential Monitoring
Data Breach Detection
Brand Protection
Threat Actor Tracking
Early Warning Alerts
Takedown Assistance
Early breach detection
Prevent account takeovers
Protect brand reputation
Proactive threat intelligence
Connect With Us
DPDP Compliance
2M+
Data Principals Covered
5,000+
DSRs Processed
< 72 hrs
Avg Grievance Response

DPDP Compliance

Digital Personal Data Protection Act, 2023

End-to-end support to build a DPDP Act-compliant data protection program — from consent management to data principal rights and breach readiness.
Consent Management
Data Mapping & Classification
Data Principal Rights (DSR)
Breach Notification (72-hr)
Data Protection Impact Assessment
Cross-Border Transfer Compliance
Build a DPDP Act, 2023-compliant data protection program
Implement consent management and data principal rights workflows
Reduce regulatory risk with documented DPIAs and breach playbooks
Board-ready compliance reporting and audit trails
Know More
Red Teaming
300+
Attack Scenarios Simulated
1,200+
Critical Findings Uncovered
85%
Objectives Achieved

Red Teaming

Adversary Emulation & Attack Simulation

Full-scope, objective-driven attack simulations that test your organization's real-world detection and response capability against a determined adversary.
Adversary Simulation
Exploit Development
C2 & Persistence Testing
Lateral Movement Assessment
Detection Evasion Testing
Purple Team Debrief
Test real-world detection and response capability, not just vulnerabilities
Validate security investments against a determined adversary
Uncover gaps across people, process, and technology
Detailed adversary emulation report mapped to MITRE ATT&CK
Know More
Blue Teaming
3,500+
Incidents Contained
< 10min
Mean Time to Detect
95%
Detection Coverage

Blue Teaming

Detection Engineering & Defense Operations

Build and mature your defensive capability — from detection engineering and SOC playbooks to real-time threat monitoring and incident response.
Threat Detection Engineering
SOC Playbook Development
SIEM/EDR Rule Tuning
Incident Triage & Response
Threat Hunting
Automated Response Playbooks
Strengthen detection engineering and SOC playbooks
Reduce mean time to detect and respond to real threats
Continuously tune SIEM/EDR rules against evolving TTPs
Build in-house defensive maturity, not just outsourced monitoring
Know More
ISO 27001 Implementation
120+
Organizations Certified
93
Annex A Controls Mapped
100%
Audit Pass Rate

ISO 27001 Implementation

ISMS Design, Implementation & Certification Support

Build a right-sized Information Security Management System and get hands-on support all the way through external ISO/IEC 27001:2022 certification audit.
Gap Assessment
Policy & SOA Documentation
ISMS Framework Design
Risk Assessment & Treatment
Access Control Implementation
Certification Audit Support
Achieve ISO/IEC 27001:2022 certification with expert guidance
Build a right-sized ISMS mapped to your actual risk profile
Full Annex A control implementation and Statement of Applicability
Hands-on support through external certification audit
Know More
SOC 2 Type I & Type II
80+
SOC 2 Reports Delivered
5/5
Trust Criteria Covered
6-12 mo
Avg Type II Window

SOC 2 Type I & Type II

Assessment & Implementation

Get audit-ready for SOC 2 Type I and Type II — control design, evidence collection, and continuous monitoring mapped to all five Trust Services Criteria.

Cloud Controls Assessment
Type I Readiness Assessment
Type II Continuous Monitoring
Evidence Collection & SOC Report
Security Trust Criteria
Availability & Process Integrity
Prepare for and pass SOC 2 Type I and Type II audits
Map controls to all five Trust Services Criteria
Automate evidence collection for continuous audit readiness
Build customer trust for enterprise and regulated deals
Know More

Additional Security Services

Complementary services to strengthen your security posture

Compliance & Audit

ISO 27001, SOC 2, HIPAA, PCI DSS, GDPR compliance assessments and audit support

Data Security & Privacy

Data classification, encryption, DLP, and DSPM solutions for sensitive data protection

Security Architecture

Design and implementation of comprehensive security frameworks and architectures

Security Awareness Training

Employee training programs including phishing simulations and security best practices

Ready to Secure Your Organization?

Let's discuss your security needs and create a tailored solution for your business. Our experts are ready to help.